September 29, 2026

Editor's Choice

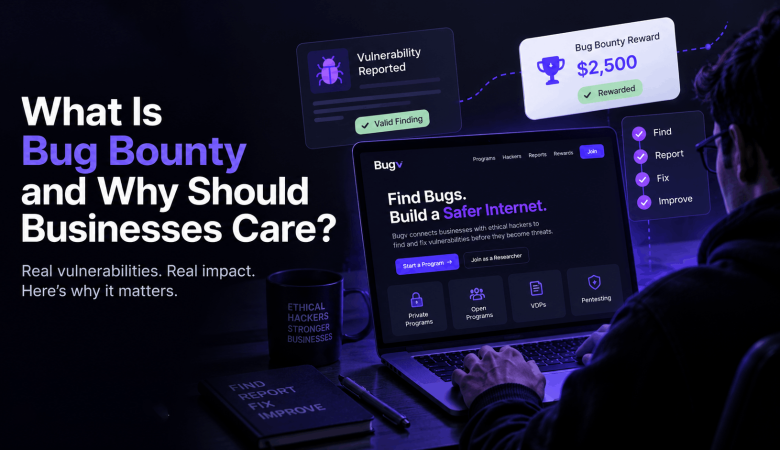
What Is Bug Bounty and Why Should Businesses Care?

Your security team can test your systems. But what happens when hundreds of ethical hackers are looking too? That...
The Hidden Cybersecurity Risk Behind Your Banking App

You open your banking app, enter your credentials, check your balance, and transfer money. From your perspective, it feels...

Can AI Replace Ethical Hackers?

Artificial Intelligence (AI) is transforming cybersecurity at an unprecedented pace. From identifying suspicious activity to automating threat detection and...

KrispCall Launches Public Bug Bounty Program on Bugv

As cyber threats continue to evolve, organizations are increasingly recognizing that cybersecurity is not just about prevention—it's about continuous...

banner-student-ambassador-program

Bugv Student Ambassador Program: Empowering the Next Generation of Cybersecurity Leaders

As technology continues to evolve, cybersecurity has become one of the most important skills of the digital era. From...

The Ethics of Hacking: What Separates Black Hat from White Hat?

Hacking has long been a term shrouded in controversy, often misunderstood by the public due to its portrayal in...

Zero-Day Vulnerabilities Explained: How They’re Discovered, Exploited & Patched

A zero-day vulnerability is one of the most dangerous threats in cybersecurity unknown to the vendor, unpatched, and actively weaponizable. Understanding how they...

The Rise of Crowdsourced Security in South Asia: 2020–2025 Growth Story

South Asia is undergoing a quiet but consequential transformation in how organisations defend their digital infrastructure. The shift from traditional, point-in-time security audits...

What Every Bug Bounty Hunter in Nepal Needs to Know. 

The possession of the proper tools does not turn you into a good bug bounty hunter. Knowing what those tools are and by...

OWASP Top 10 Explained With Bugv Examples 

The most commonly used list of security risks that are considered critical to web applications is the OWASP Top 10. The Open Worldwide Application...

SQL Injection 2026: Still There, Still a Serious Problem

The general belief within the security community is that SQL Injection is an obsolete issue that was fixed back in the early 2000s...

The Most Common Vulnerabilities Found in Early-Stage Startups (And How to Avoid Them) 

Startups are fast moving- and you can see why not. However, as usual, speed is the distinction between growth and irrelevance. However, when...